News analysis ·
SIM-swap crypto theft: how a London case worked
A London man was jailed over SIM-swap thefts of crypto from four victims. We explain how the attack works, what it bypasses and how to reduce the risk.
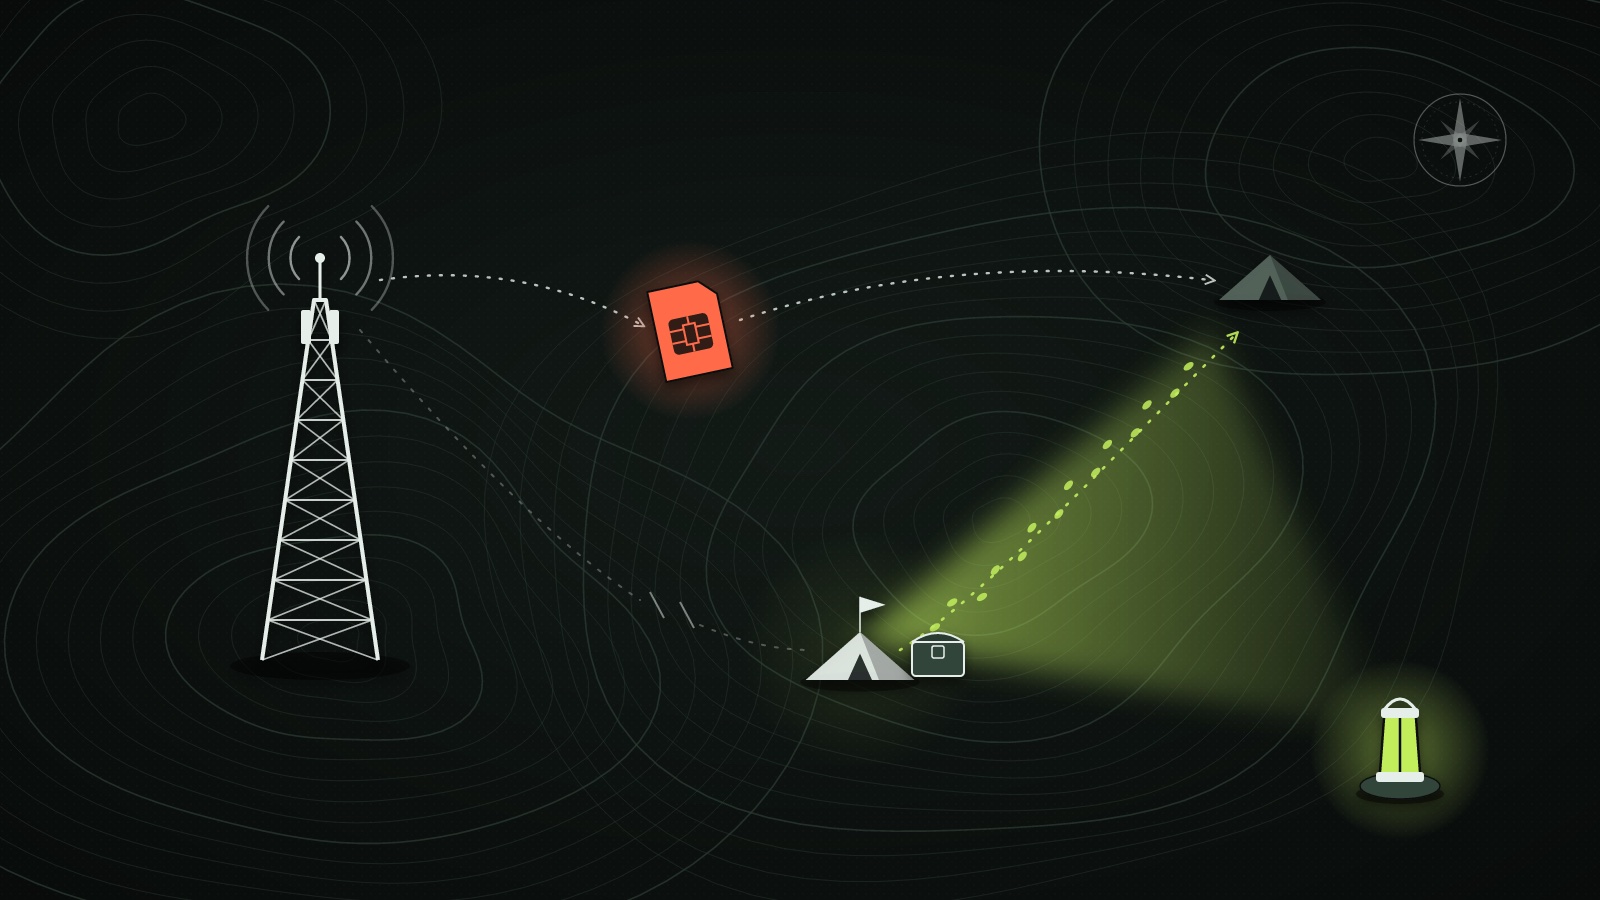
A court in London has handed a two and a half year jail term to a man over SIM-swap thefts that took almost £200,000 ($265,000) in cryptocurrency, Decrypt reported, citing City of London Police. The case is a clear example of an attack that never touches a blockchain's code. This article looks at how the scheme worked, why text message codes were the weak point, and what defences experts suggest.
What the case shows
According to Decrypt, Ajay Shinjin, 25, who also goes by AJ Marley Cruz, received the sentence at Inner London Crown Court. On September 28 he had pleaded guilty to two charges: a fraud conspiracy involving false representation, and moving criminal property.
Police said more than £44,000 of the haul ended up with him personally. It paid for Dubai holidays, gold-plated teeth grills and a flat in Canary Wharf. A City of London Police officer, Detective Constable Simon Ardeman, put the wider problem this way: "SIM-swap fraud is a sophisticated and increasingly concerning form of offending".
The losses fell on four victims. One had about £40,000 of crypto taken on November 2, 2021, and roughly £27,000 of that reached Shinjin's own crypto account. A second victim's roughly £17,000 went entirely to his wallet. He also helped take about £8,000 held on Coinbase by a third person, and about £130,000 from a fourth.
The method: taking over a phone number
A SIM swap moves a victim's phone number onto a SIM card that the attacker controls. From that moment, calls and text messages meant for the victim arrive on the criminal's phone. That includes the one-time codes that many banks and crypto platforms text out to confirm a login or a withdrawal.
The important point is what the attacker does not need. There is no need to break the exchange's systems or guess a private key. If an account relies on a text message as its second factor, control of the number can be enough to reset a password, pass a login check and approve a transfer.
In this case, Decrypt reported that BT spotted unauthorized activity in its own systems in early November 2021, through which customer numbers had been shifted to SIM cards held by criminals. The company then traced the devices that received the numbers, and its data pointed police to several suspects. Shinjin was tied to four of those devices.
How the investigation unfolded
The case took years to close. Police first arrested Shinjin at home in 2021. He was arrested again at Heathrow Airport in October 2023 as he returned from Dubai, after new evidence emerged. In police interviews he declined to comment.
The trail here ran through telecom records and device data, not only through wallet addresses. That is a useful reminder for anyone studying crypto crime: the on-chain record shows where coins went, but linking an address to a person often depends on off-chain evidence such as carrier logs, devices and exchange account details.
Limits: what this one case does and does not tell us
A single court case is a narrow window on a wider problem.
- The figures are the amounts police and court records attribute to this defendant; they do not measure total SIM-swap losses.
- The case concerns accounts at platforms that used phone-based checks, so it says little about wallets where users hold their own keys.
- Wider statistics depend on what gets reported. Fraud prevention service Cifas said in August that unauthorized SIM swap cases logged in UK national fraud records jumped 402% in the first half of 2026 versus a year earlier, but recorded cases are not the same as all attempts.
- The thefts date back to 2021, and carrier and platform defences may have changed since then.
Cifas linked the rise to SIM swaps being used more often to catch security codes and get around account protections, which matches the pattern in this case.
What to watch and how to reduce the risk
The advice reported by Decrypt focuses on removing the phone number as a single point of failure. Mark Birchall, a cybersecurity editor at Norton, suggests using an authenticator app for two-factor login instead of text messages. An app links access to the phone itself, not to a number that can be moved.
Birchall also recommends asking your mobile carrier for a separate PIN or passcode, and turning on account takeover protection where carriers offer it. These steps make it harder for someone to move your number without extra checks.
- Check which of your exchange and email accounts still use text messages for login or withdrawals.
- Treat your email account as part of your crypto security, since password resets often go there.
Sources
- Decrypt, 9 Oct 2026
Drafted by AI from the research and on-chain sources listed, then published automatically once checks confirmed the figures against those sources and found no copied text. Not reviewed by a person. Metrics are explained, never turned into price calls.